BNKSecPolicy
BNKSecPolicy was developed according to the Gateway Enhancement Proposal (GEP: 2648). BNKSecPolicy CRD, a BNKGateway extension (gateway.k8s.f5net.com), attaches security policies, such as ACL policies (F5BigFwPolicy), DOS Policies (F5BigDdosGlobal) and F5BigLogProfile to Gateway API objects. The YAML file defines a CustomResourceDefinition (CRD) for Kubernetes to create and manage custom resources with the specified schema and behavior.
The specification section in the YAML file includes these two arrays:
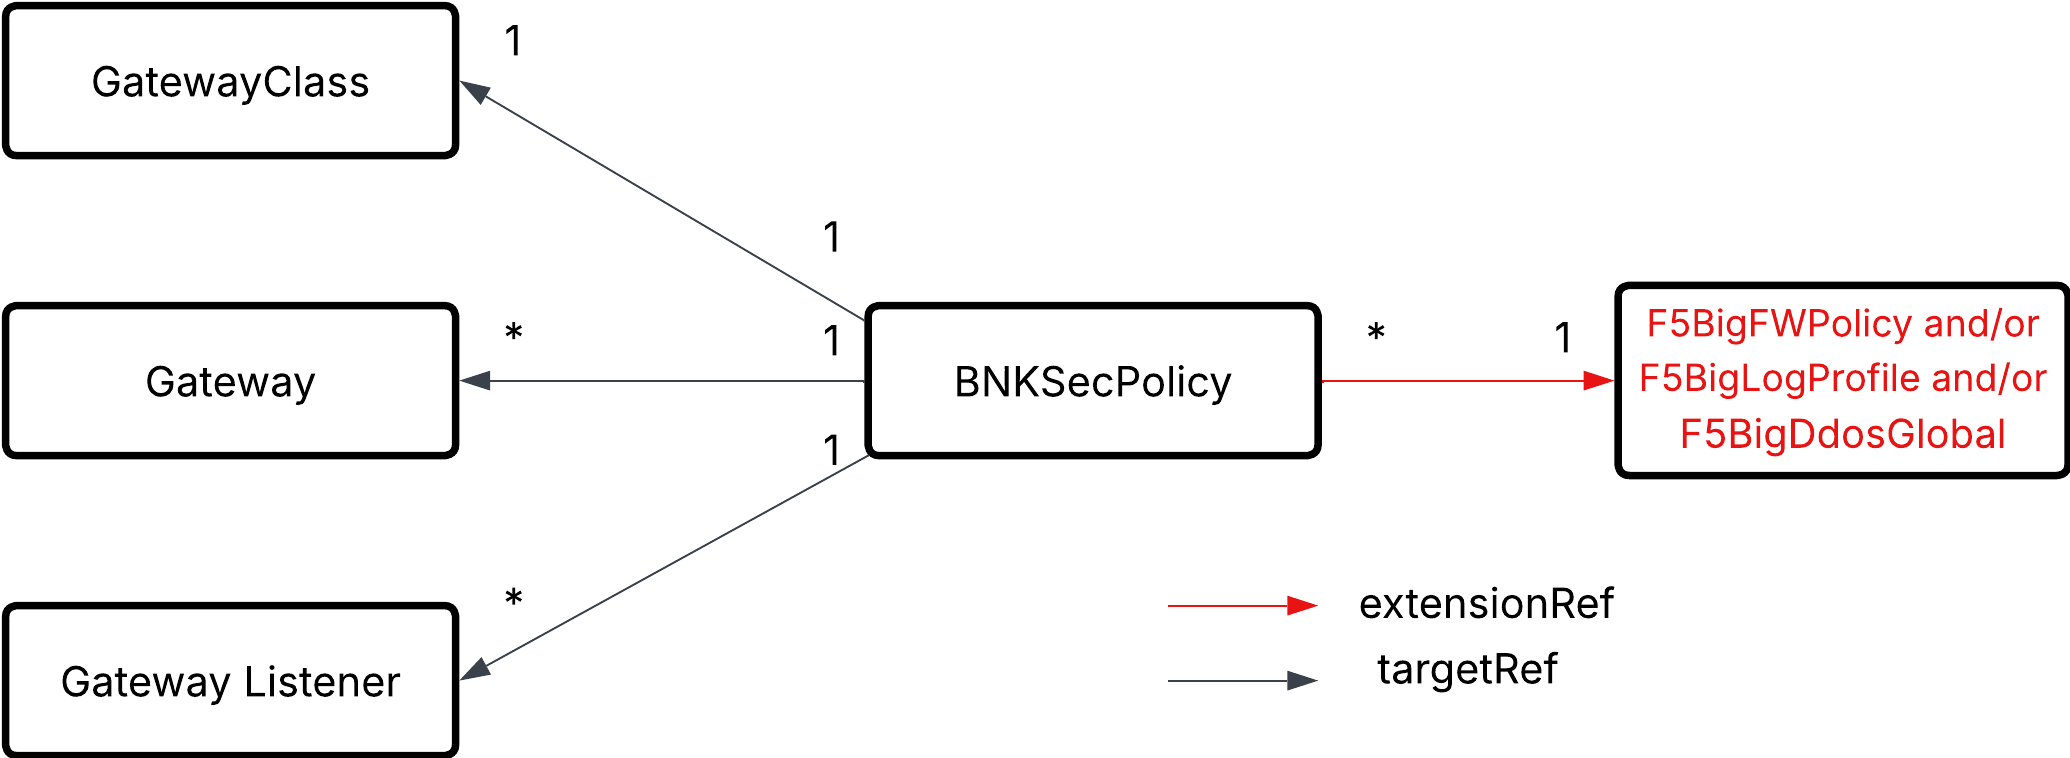
extensionRefs: Represents external resource configurations (For example, F5BigFwPolicies) that apply to specific Gateway resources in the cluster.targetRefs: Specifies Gateway/Gateway Listener/GatewayClass resources that will receive the configurations from the extensionRefs.
According to GEP: 2648, the status.ancestors section is implemented to show the status of targetRefs attachments.
Note
Perform Custom Resource (CR) operations only when the controller is in a running state.
Design rules
A BNKSecPolicy can be attached to multiple objects using the targetRefs array field. However, BNKSecPolicy can be attached only to one GatewayClass.
A BNKSecPolicy with extensionRef F5BigDdosGlobal can be attached to targetRef GatewayClass only.
A Target (GatewayClass, Gateway, or Gateway Listener) can only have one BNKSecPolicy attached to it. If multiple BNKSecPolicies are attached to the same target, it will create a conflict. In such cases, the conflict should be resolved based on the “oldest by creation date wins” policy, as outlined in GEP-2648.
A BNKSecPolicy CR must include F5BigFwPolicy/F5BigDdosGlobal/F5BigLogProfile item in the extensionRefs array.
The same F5BigFwPolicy or F5BigLogProfile can be referenced in multiple BNKSecPolicy CRs.
A maximum of 16 targetRefs can be defined in a single BNKSecPolicy.
The BNKSecPolicy CR supports general extensions. The CR can reference resources such as F5BigFWPolicy, F5BigDdosGlobal and F5BigLogProfile. This image illustrates the scope of the BNKSecPolicy CR.
CR Parameters
This section provides a description and default value of the parameters in the BNKSecPolicy CR.
metadata
Parameter |
Description |
|---|---|
|
The unique name identifying the resource. Example: |
|
The Kubernetes namespace in which the policy object is applied. It can be the CNE Controller’s namespace (e.g. f5-bnk) or the application namespace. |
spec
Parameter |
Type |
Description |
Default |
|---|---|---|---|
|
array |
Array of references to extension resources that should be applied to the |
|
|
string |
API group of the referenced extension resource. Max length 255. Pattern: |
|
|
string |
Kind of the referenced extension resource. Allowed values: |
(none) |
|
string |
Name of the referenced extension resource. Max length 255. Pattern: |
(none) |
|
array |
Array of references to resources the |
(none) |
|
string |
API group of the target resource. Max length 255. Pattern: `^$ |
|
|
string |
Kind of the target resource. Allowed values: |
|
|
string |
Name of the target resource. Min length 1, max length 255. Pattern: |
(none) |
|
string |
Section within the target. For |
|
status
The status section is controller-populated and shows current state of F5BnkSecPolicy.
Parameter |
Type |
Description |
Default |
|---|---|---|---|
|
array |
List of ancestor resources (usually Gateways) that are targets of the policy, plus conditions indicating attachment/status per ancestor. |
(none) |
|
array |
List of descendant/extension resources associated with the policy, plus conditions indicating status per descendant. |
(none) |
Spec validation rules (from CRD)
Rule |
Effect |
|---|---|
If |
Prevents attaching |
|
|
|
Avoids duplicate target entries with same section. |
Per-item: if |
Enforces GatewayClass restriction. |
Samples of status section
The status section shows the current state of F5BnkSecPolicy.
F5BnkSecPolicy with F5BigLogProfile attached to Gateway
Sample F5BnkSecPolicy CR with F5BigLogProfile attached to Gateway:
apiVersion: gateway.k8s.f5net.com/v1alpha1
kind: BNKSecPolicy
metadata:
  name: bnksecpolicy-gateway
  namespace: gatewayns
spec:
  extensionRefs:
  - group: k8s.f5net.com
    kind: F5BigLogProfile
    name: logprofile
  targetRefs:
  - group: gateway.networking.k8s.io
    kind: Gateway
    name: f5-gateway
    sectionName: ""
The status section in this YAML code provides ancestors block to indicate the success state of the custom resource.
status:
  ancestors:
  - ancestorRef:
      group: gateway.networking.k8s.io
      kind: Gateway
      name: f5-gateway
      namespace: gatewayns
    conditions:
    - lastTransitionTime: "2026-03-18T09:00:16Z"
      message: Gateway CR "gatewayns"/"f5-gateway" exists
      observedGeneration: 1
      reason: ResolvedRef
      status: "True"
      type: ResolvedRefs
    controllerName: f5.com/f5-bnk-f5-cne-controller
  descendants:
  - conditions:
    - lastTransitionTime: "2026-03-18T08:58:41Z"
      message: F5BigLogProfile CR "gatewayns"/"logprofile" exists
      observedGeneration: 1
      reason: ResolvedRef
      status: "True"
      type: ResolvedRefs
    descendantRef:
      group: k8s.f5net.com
      kind: F5BigLogProfile
      name: logprofile
F5BnkSecPolicy with F5BigFWPolicy attached to Gateway Listener
Sample F5BnkSecPolicy CR with F5BigLogProfile attached to Gateway:
apiVersion: gateway.k8s.f5net.com/v1alpha1
kind: BNKSecPolicy
metadata:
  name: bnksecpolicy-gateway
  namespace: gatewayns
spec:
  extensionRefs:
  - group: k8s.f5net.com
    kind: F5BigFwPolicy
    name: firewallpolicy-gateway
  targetRefs:
  - group: gateway.networking.k8s.io
    kind: Gateway
    name: f5-gateway
    sectionName: tcp-listener
The status section in this YAML code provides ancestors and descendants blocks to indicate the success state of the custom resource.
status:
  ancestors:
  - ancestorRef:
      group: gateway.networking.k8s.io
      kind: Gateway
      name: f5-gateway
      namespace: gatewayns
      sectionName: tcp-listener
    conditions:
    - lastTransitionTime: "2026-03-18T09:00:16Z"
      message: Gateway CR "gatewayns"/"f5-gateway" exists
      observedGeneration: 1
      reason: ResolvedRef
      status: "True"
      type: ResolvedRefs
    controllerName: f5.com/f5-bnk-f5-cne-controller
  descendants:
  - conditions:
    - lastTransitionTime: "2026-03-18T08:58:41Z"
      message: F5BigFwPolicy CR "gatewayns"/"firewallpolicy-gateway" exists
      observedGeneration: 1
      reason: ResolvedRef
      status: "True"
      type: ResolvedRefs
    descendantRef:
      group: k8s.f5net.com
      kind: F5BigFwPolicy
      name: firewallpolicy-gateway
F5BnkSecPolicy with F5BigDdosGlobal attached to GatewayClass
Sample F5BnkSecPolicy CR with F5BigDdosGlobal attached to GatewayClass:
apiVersion: "gateway.k8s.f5net.com/v1alpha1"
kind: BNKSecPolicy
metadata:
  name: bnksecpolicy-gatewayclass
  namespace: f5-bnk
spec:
  extensionRefs:
    - name: gateway-global-ddos
      group: k8s.f5net.com
      kind: F5BigDdosGlobal
  targetRefs:
    - name: f5-gateway-class
      kind: GatewayClass
      group: gateway.networking.k8s.io
The status section in this YAML code provides ancestors and descendants blocks to indicate the success state of the custom resource.
status:
  ancestors:
  - ancestorRef:
      group: gateway.networking.k8s.io
      kind: GatewayClass
      name: f5-gateway-class-1
      namespace: f5-bnk
    conditions:
    - lastTransitionTime: "2026-03-18T09:57:26Z"
      message: GatewayClass CR "f5-gateway-class-1" exists
      observedGeneration: 1
      reason: ResolvedRef
      status: "True"
      type: ResolvedRefs
    controllerName: f5.com/f5-bnk-f5-cne-controller
  descendants:
  - conditions:
    - lastTransitionTime: "2026-03-18T09:57:26Z"
      message: F5BigDdosGlobal CR "f5-bnk"/"gateway-global-ddos" exists
      observedGeneration: 1
      reason: ResolvedRef
      status: "True"
      type: ResolvedRefs
    descendantRef:
      group: k8s.f5net.com
      kind: F5BigDdosGlobal
      name: gateway-global-ddos