NetPolicy
Overview
NetPolicy is a new adapter CRD created using the policy attachment pattern. When the NetPolicy CR is applied, it creates the policy object by linking the specified BNK custom resources (such as F5BigCneIrule or F5BigPersistenceProfile) with the Kubernetes Gateway API CRDs.
The specification section in the YAML file of NetPolicy CR must include these two arrays:
extensionRefs: Represents external resource configurations (For example, F5BigCneIrule) that apply to a Gateway or specific listener.targetRefs: Specifies Gateway that will receive the configurations from the extensionRefs.
Note
You cannot modify the targetRefs field after you create the custom resource (CR). To change the target Gateway, delete the existing NetPolicy CR and create a new one with the updated target.
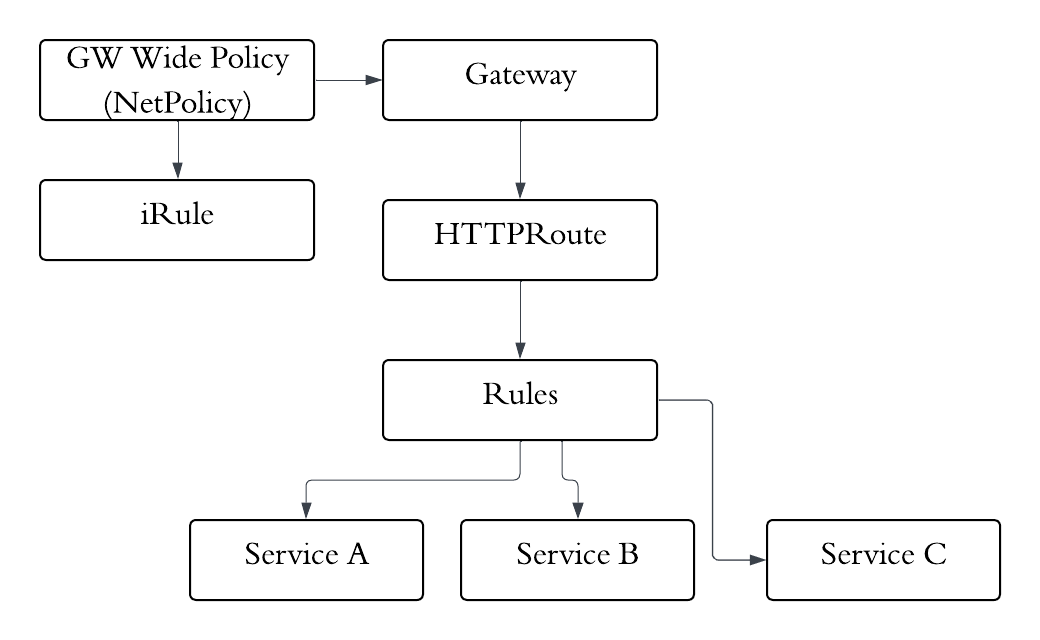
This diagram shows the flow of traffic and the role of policies, iRules, and Gateway API components within the system.
CR Parameters
The sections and the list of parameters to define the NetPolicy CR.
metadata
Parameter |
Description |
|---|---|
name |
The unique name identifying the resource. For example, my-test-netpolicy |
namespace |
The namespace of Kubernetes in which the policy is applied. Refers to Gateway API policy attachment. For example, |
spec
Parameter |
Description |
Default |
|---|---|---|
|
Specifies the kind of custom resource to attach. Supported values include |
F5BigCneIrule |
|
Includes |
|
|
Specifies a string value of a maximum of 255 characters that refers to an API group. |
k8s.f5net.com |
|
Specifies a string value of a maximum of 255 characters that refers to the name of the resource. |
|
|
Specifies the kind of resource. The maximum length of the string is 63. Options are Irule or PersistenceProfile.” |
|
|
|
|
|
Specifies the API group referencing the Kubernetes Networking Gateway API. It can have a maximum of 255 characters. |
gateway.networking.k8s.io |
|
Specifies the name of the resource. It can have a maximum of 255 characters. |
|
|
Specifies the kind of resource. |
Gateway |
|
Specifies the string value of a maximum of 253 characters that indicates the specific listeners in the gateway. |
“” |
status
The status section in NetPolicy defines the current status of ancestors and descendants.
Parameter |
Description |
|---|---|
|
Ancestors is a list of ancestor resources (usually Gateways) that are linked to the policy. It shows the policy’s status with respect to each ancestor. |
|
Descendants is a list of descendant resources (extensionRefs) that are linked to the policy. It shows the policy’s status with respect to each descendant. |
Design rules
Multiple Netpolicies
How to apply:
You can apply multiple BIG-IP Next for Kubernetes Net Policies to a single gateway only when
A policy is applied at the gateway level to define global network behavior for the gateway.
A policy is applied at the listener level by specifying the targetRefs.sectionName in the NetPolicy CR to target specific listeners in Gateway configuration.
For example:
When there are three policies (NetPolicy1, NetPolicy2, and NetPolicy3) you can
Apply NetPolicy1 to gateway.
Apply NetPolicy2 to listener1 (http_service).
Apply NetPolicy3 to listener2 (dns_service).
How not to apply:
Multiple NetPolicies cannot be applied when,
Multiple policies are applied at the same listener level. This results in conflicting behavior at the specific listener.
Multiple policies are applied at the gateway level. A gateway cannot have conflicting global configurations.
For example:
When there are three policies (NetPolicy1, NetPolicy2, and NetPolicy3) you cannot apply two policies (NetPolicy1 and NetPolicy2) to a gateway.
Execution Order:
When multiple policies are applied, and traffic passes through the gateway, the gateway-level iRule is executed first, followed by the listener-level iRule.
For example
When traffic flows through listener1, an iRule applied at the Gateway level is executed first, followed by an iRule applied to listener1.
When traffic flows through listener2, an iRule applied at the Gateway level is executed first, followed by an iRule applied to listener2.
The NetPolicy CR supports general extensions. This CR can reference resources such as iRules.
For details on iRule application in NetPolicy, see F5 iRule in NetPolicy
Configure NetPolicy
Prerequisites
Make sure,
The product BNK (DPU) is installed and the F5 controller is running.
The GatewayClass CR is configured.
The Gateway CR is configured.
The F5BigCneIrule CR is created.
NetPolicy with F5BigCneIrule attached to Gateway
Apply F5BigCneIrule CR
  apiVersion: k8s.f5net.com/v1
  kind: F5BigPersistenceProfile
  metadata:
    name: persistence-profile-one
    namespace: gatewayns
  spec:
    persistenceType: MODEL_CONTEXT_PROTOCOL
    timeout: 300
kubectl create -f irule.yaml
f5bigcneirule.k8s.f5net.com/irule-one created

kubectl get -f irule.yaml
NAME        READY   MESSAGE                                AGE
irule-one   True    CR config sent to all grpc endpoints   3m37s
Apply NetPolicy CR
apiVersion: "gateway.k8s.f5.com/v1alpha1"
kind: NetPolicy
metadata:
  name: my-test-netpolicy
  namespace: gatewayns
spec:
  extensionRefs:
  - kind: F5BigCneIrule
    name: irule-one
    group: k8s.f5net.com
  targetRefs:
  - kind: Gateway
    name: my-l4route-tcp-gateway
    group: gateway.networking.k8s.io
    sectionName: "l4-nginx-tcp"
kubectl create -f NetPolicy.yaml
NetPolicy.gateway.k8s.f5.com/my-test-netpolicy created

kubectl get -f NetPolicy.yaml
NAME                AGE
my-test-netpolicy   6s
Note
NetPolicy, Gateway, F5BigCneIrule CRs should be in the same namespace when attached to Gateway or Gateway Listener.
NetPolicy with F5BigPersistenceProfile attached to Gateway
Apply F5BigPersistenceProfile CR
apiVersion: k8s.f5net.com/v1
kind: F5BigPersistenceProfile
metadata:
  name: cnf-mcp-persistence
  namespace: gatewayns
spec:
  persistenceType: MODEL_CONTEXT_PROTOCOL
  mcpEncryptionPassphrase:
    secretRef:
      name: mcp-crypto-vault
      passphraseField: primary-passphrase
kubectl create -f persistence-profile.yaml
f5bigpersistenceprofile.k8s.f5net.com/cnf-mcp-persistence created
kubectl get -f persistence-profile.yaml
NAME                   READY   MESSAGE                                AGE
cnf-mcp-persistence    True    CR config sent to all grpc endpoints   1m15s
Apply NetPolicy CR
apiVersion: "gateway.k8s.f5.com/v1alpha1"
kind: NetPolicy
metadata:
  name: my-test-netpolicy
  namespace: gatewayns
spec:
  extensionRefs:
  - kind: F5BigCneIrule
    name: irule-one
    group: k8s.f5net.com
  targetRefs:
  - kind: Gateway
    name: my-l4route-tcp-gateway
    group: gateway.networking.k8s.io
    sectionName: "l4-nginx-tcp"
kubectl create -f NetPolicy-persistence.yaml
NetPolicy.gateway.k8s.f5.com/persistence-netpolicy created
kubectl get -f NetPolicy-persistence.yaml
NAME                    AGE
persistence-netpolicy   8s