F5 Application Delivery Controller Solutions > BIG-IP Security Essentials > Middle Layer – Authentication and Protocol Hardening > Lab Source | Edit on
API Access Control – Role-Based Enforcement (AS3 & Declarative Onboarding)
The Middle Layer enforces authentication and authorization controls over the BIG-IP control plane. This lab validates secure access to service extensions (AS3 and Declarative Onboarding) using role-based authorization and deterministic REST validation.
This lab assumes:
Network-layer segmentation (Outer Layer) is enforced.
Administrative authentication (MFA) is in place or delegated to centralized AAA.
This lab focuses on authorization enforcement at the REST framework layer.
Authentication answers:
Who are you?
Authorization answers:
What are you allowed to do?
Executive Summary
This lab demonstrates secure API access enforcement for BIG-IP service extensions through layered controls:
Network segmentation (Outer Layer)
REST authentication
Role-based authorization
Device-scoped extension protection
Deterministic authorization failure behavior
Together, these controls enforce least privilege and protect declarative service extensions from unauthorized invocation.
API Exposure Surface
Endpoint Family |
Port |
Purpose |
|---|---|---|
/mgmt/shared/appsvcs/* |
TCP 443 |
AS3 service extension (device-scoped) |
/mgmt/shared/declarative-* |
TCP 443 |
Declarative Onboarding (device-scoped) |
These endpoints are exposed on the BIG-IP management interface and are protected by the REST framework’s authentication and role-based authorization.
Objective
Validate secure, deterministic API access to BIG-IP service extensions while enforcing:
Role-based authorization
Least privilege validation
Device-scoped extension protection
Management-plane isolation
Deterministic authorization failure behavior
Threat Model
This lab assumes an adversary may attempt to:
Use valid credentials with insufficient privileges to invoke device-scoped APIs.
Access the BIG-IP management API from an authorized network without sufficient privileges.
Abuse overly privileged accounts to deploy unauthorized configurations.
Invoke device-scoped service extensions (AS3/DO) using partition-scoped roles.
Submit unauthorized declarative configurations.
Controls validated in this lab mitigate these threats via:
Management-plane segmentation.
Strict REST authentication enforcement.
Role-based authorization at the REST framework layer.
Explicit denial of device-scoped extension access to non-administrative roles.
Architecture Overview
AS3 and Declarative Onboarding operate under:
/mgmt/shared/*
These endpoints are:
Device-scoped
Not partition-scoped
Protected by REST framework authorization
Not configurable for partition-level delegation
Authorization Flow:
Client authenticates using REST Basic Authentication.
REST framework validates credentials.
Authorization policy evaluates assigned role.
Service extension executes only if role permits.
Lab Environment Reference
Management IP of BIG-IP:
10.1.1.5
All API testing in this lab will target:
https://10.1.1.5
Phase 1 – Baseline Validation
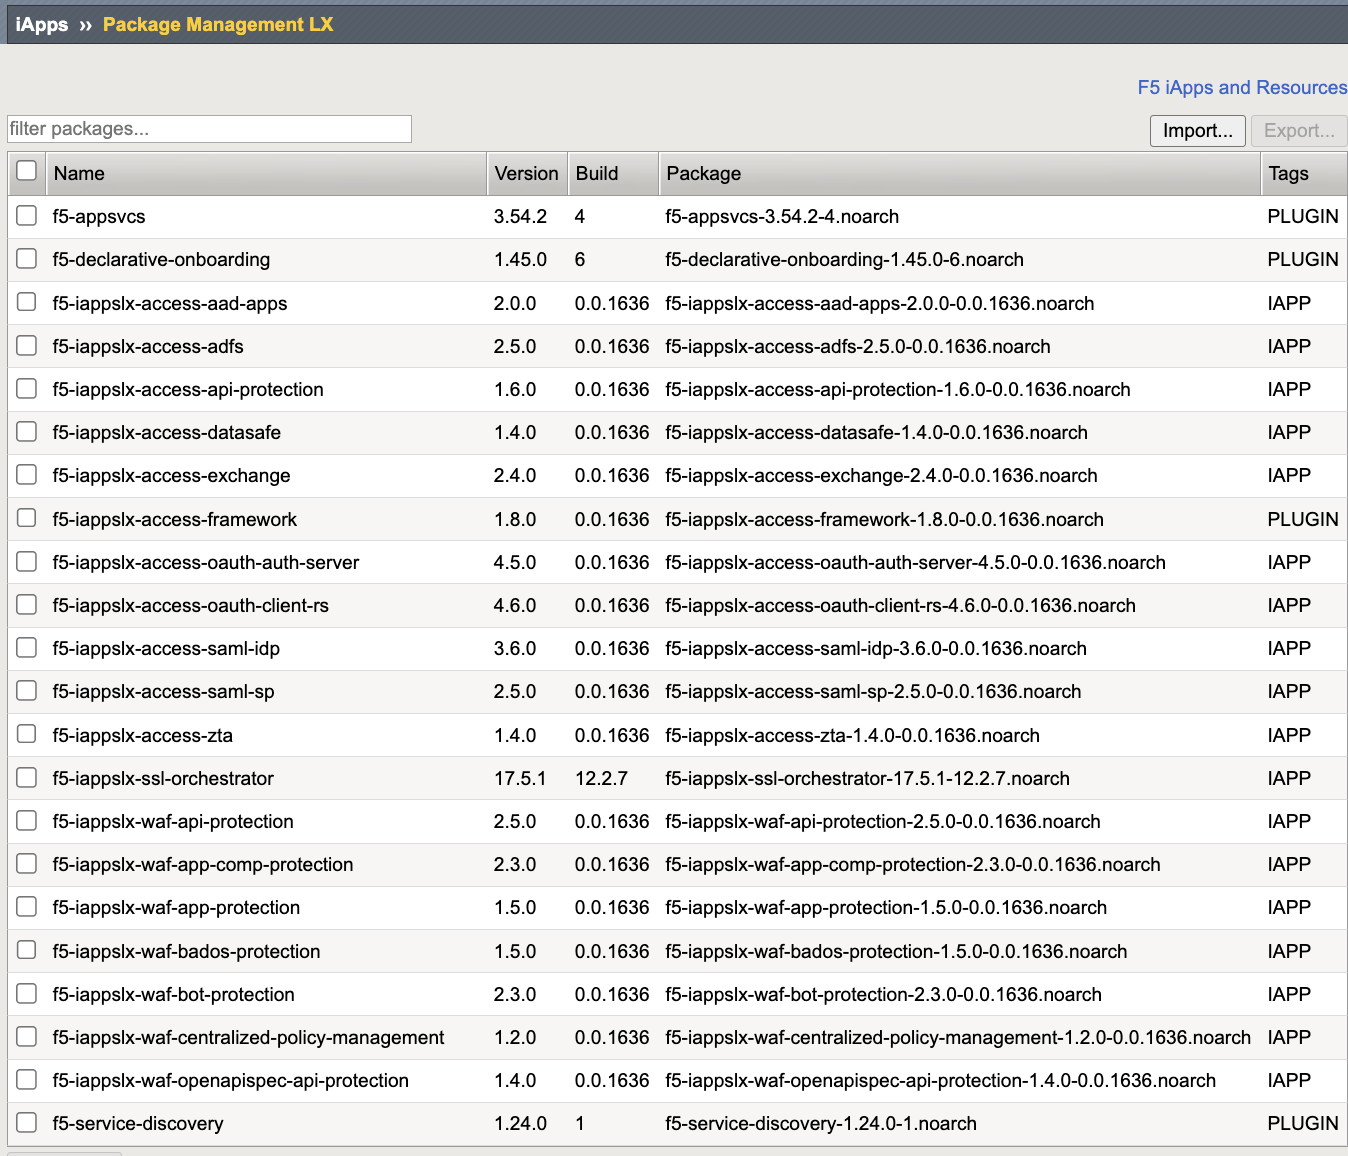
Verify AS3 and DO Installed
Navigate to:
iApps → Package Management LX
Confirm the following packages are installed:
f5-appsvcsf5-declarative-onboarding
Baseline API Reachability (Administrator)
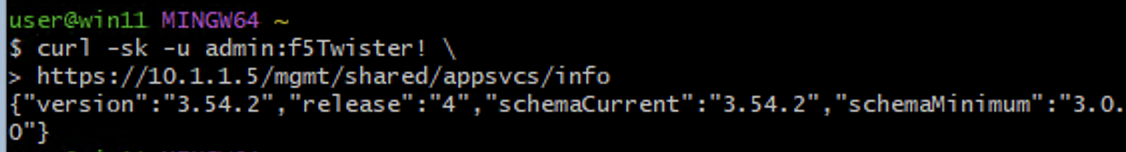
Execution Context:
Host: Windows Jump Host (10.1.1.4)
Tool: Git Bash (curl client)
Network Interface: Management Network (10.1.1.0/24)
Run the following command:
curl -sk -u 'admin:f5Twister!' \
https://10.1.1.5/mgmt/shared/appsvcs/info \
-w "\nHTTP Status: %{http_code}\n"
Expected:
HTTP Status: 200
JSON response containing AS3 version information
Phase 2 – Least Privilege Enforcement (Operator Denied)
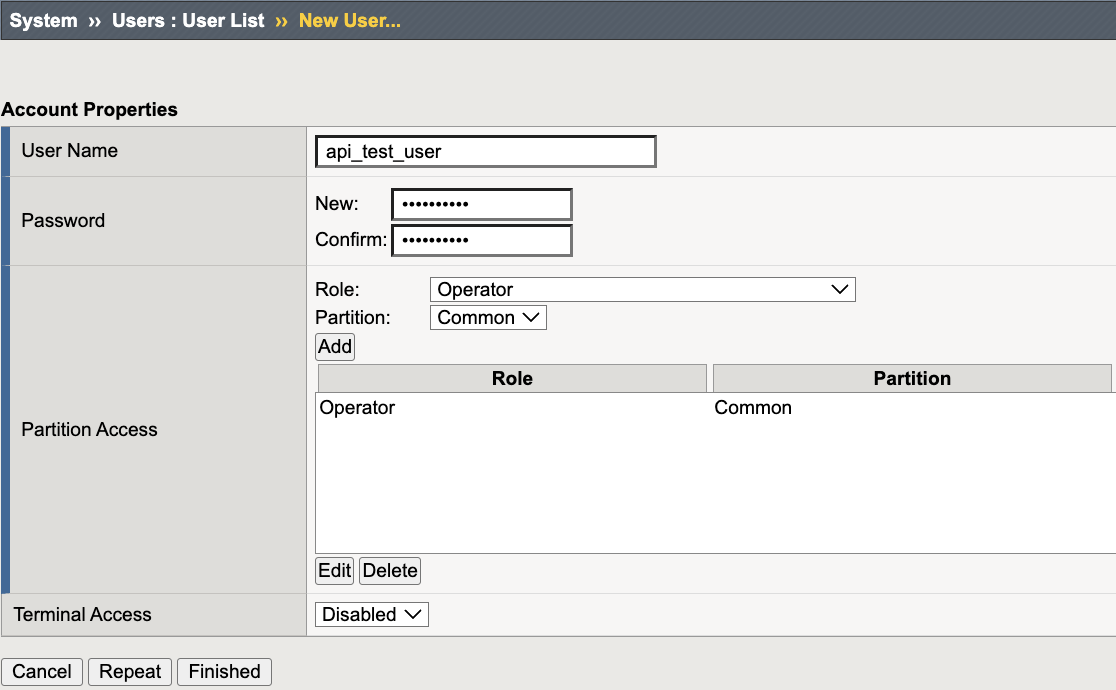
Create Restricted User
Note
When a new local user logs in for the first time, BIG-IP may require a password change. REST API authentication cannot complete this step.
Log in once through TMUI as api_test_user and change the password
before performing the API tests.
Create a local user with limited privileges:
Username:
api_test_userRole:
OperatorPartition:
CommonTerminal Access:
Disabled
Create AS3 Test Declaration (Git Bash)
Execution Context:
Host: Windows Jump Host (10.1.1.4)
Tool: Git Bash (local shell)
Network Interface: Management Network (10.1.1.0/24)
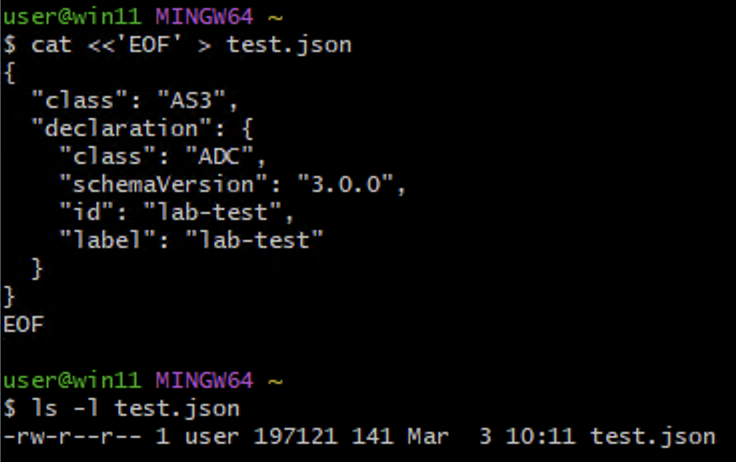
Create a minimal AS3 declaration payload locally on the jumphost. This payload is intentionally minimal and used only to validate authorization behavior.
Run the following command:
cat <<'EOF' > test.json
{
  "class": "AS3",
  "declaration": {
    "class": "ADC",
    "schemaVersion": "3.0.0",
    "id": "lab-test",
    "label": "lab-test"
  }
}
EOF
Verify file creation:
ls -l test.json
Expected:
test.jsonexists and has a non-zero size
Test AS3 Access (GET)
Execution Context:
Host: Windows Jump Host (10.1.1.4)
Tool: Git Bash (curl client)
Network Interface: Management Network (10.1.1.0/24)
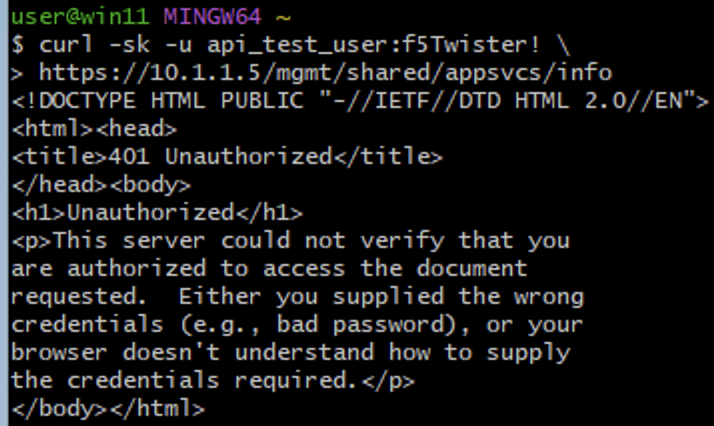
Run the following command:
curl -sk -u 'api_test_user:f5Twister!' \
https://10.1.1.5/mgmt/shared/appsvcs/info \
-w "\nHTTP Status: %{http_code}\n"
Expected:
HTTP Status: 401
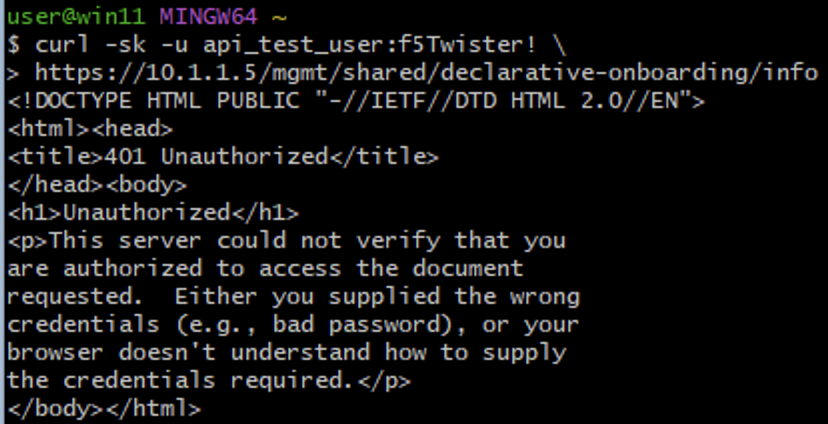
Test Declarative Onboarding Access (GET)
curl -sk -u 'api_test_user:f5Twister!' \
https://10.1.1.5/mgmt/shared/declarative-onboarding/info \
-w "\nHTTP Status: %{http_code}\n"
Expected:
HTTP Status: 401
Test AS3 Declaration Attempt (POST)
curl -sk -u 'api_test_user:f5Twister!' \
  -H "Content-Type: application/json" \
  -X POST \
  https://10.1.1.5/mgmt/shared/appsvcs/declare \
  --data-binary @test.json \
  -w "\nHTTP Status: %{http_code}\n"
Expected:
HTTP Status: 401

Why This Fails
AS3 and Declarative Onboarding operate under:
/mgmt/shared/*
These are device-scoped service extensions.
Partition-scoped roles (Operator, Application Editor) cannot invoke shared extension endpoints.
This confirms proper REST authorization enforcement.
Phase 3 – Administrative Authorization (Allowed)
Test Administrative Access
Execution Context:
Host: Windows Jump Host (10.1.1.4)
Tool: Git Bash (curl client)
Network Interface: Management Network (10.1.1.0/24)
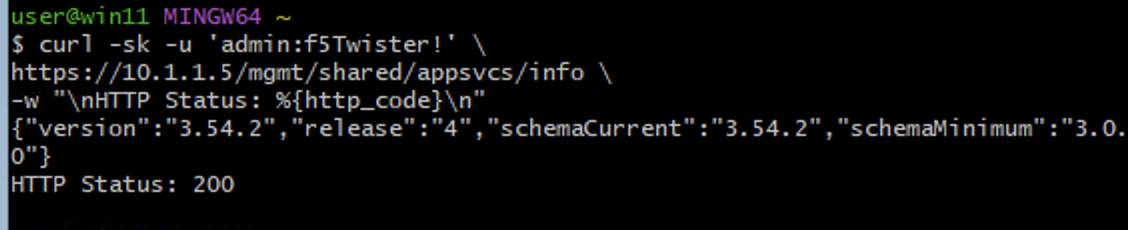
Run the following command:
curl -sk -u 'admin:f5Twister!' \
https://10.1.1.5/mgmt/shared/appsvcs/info \
-w "\nHTTP Status: %{http_code}\n"
Expected:
HTTP Status: 200
JSON response returned
Authorization Enforcement Validation Matrix
Test Case |
Expected Result |
|---|---|
Operator GET AS3 info |
HTTP 401 |
Operator GET DO info |
HTTP 401 |
Operator POST AS3 declare |
HTTP 401 |
Administrator GET AS3 info |
HTTP 200 |
Security Controls Validated
Control |
Validated |
|---|---|
REST authentication enforcement |
✔ |
Role-based authorization enforcement |
✔ |
Device-scoped extension protection |
✔ |
Least privilege validation |
✔ |
Deterministic failure behavior |
✔ |
Middle Layer Cohesion
Within the Middle Layer:
MFA validates administrative identity.
TLS enforces secure transport.
API Access Control enforces privilege boundaries.
Together, these controls prevent credential abuse, transport downgrade, and unauthorized configuration deployment.
Success Criteria
Operator role denied access to device-scoped endpoints
Administrator role permitted access
HTTP 401 returned for unauthorized requests
No configuration changes occur for denied attempts
Deterministic privilege boundary confirmed