Gateway API
Gateway API is an open‑source project from the SIG-NETWORK. It provides a collection of resources that model service networking in Kubernetes. These resources — GatewayClass, Gateway, HTTPRoute, and others, along with the Kubernetes Service resource — create an expressive, extensible, role‑based framework for consistent service networking across vendors.
BIG-IP Next for Kubernetes uses Gateway API custom resources (CRs) to route low‑latency TCP and UDP application traffic between networks through a virtual server and load‑balancing pool.
Benefits of Gateway API
Role‑oriented
Gateway API defines resource types based on organizational roles that interact with Kubernetes networking:
Infrastructure Provider: Manages shared infrastructure for multi‑tenant environments, such as cloud platforms.
Cluster Operator: Manages clusters, including policies, network access, and application permissions.
Application Developer: Manages applications running in the cluster and configures routing and service composition.
Portable
Gateway API uses custom resources. Many vendors support these CRs, which increases portability across platforms.
Expressive
Gateway API supports advanced routing features such as header matching and traffic weighting. These features previously required custom Ingress annotations.
Extensible
Gateway API allows custom resources at different layers. This makes it easier to extend routing, security, or traffic behavior without introducing complexity.
Introduction to Roles in Gateway API
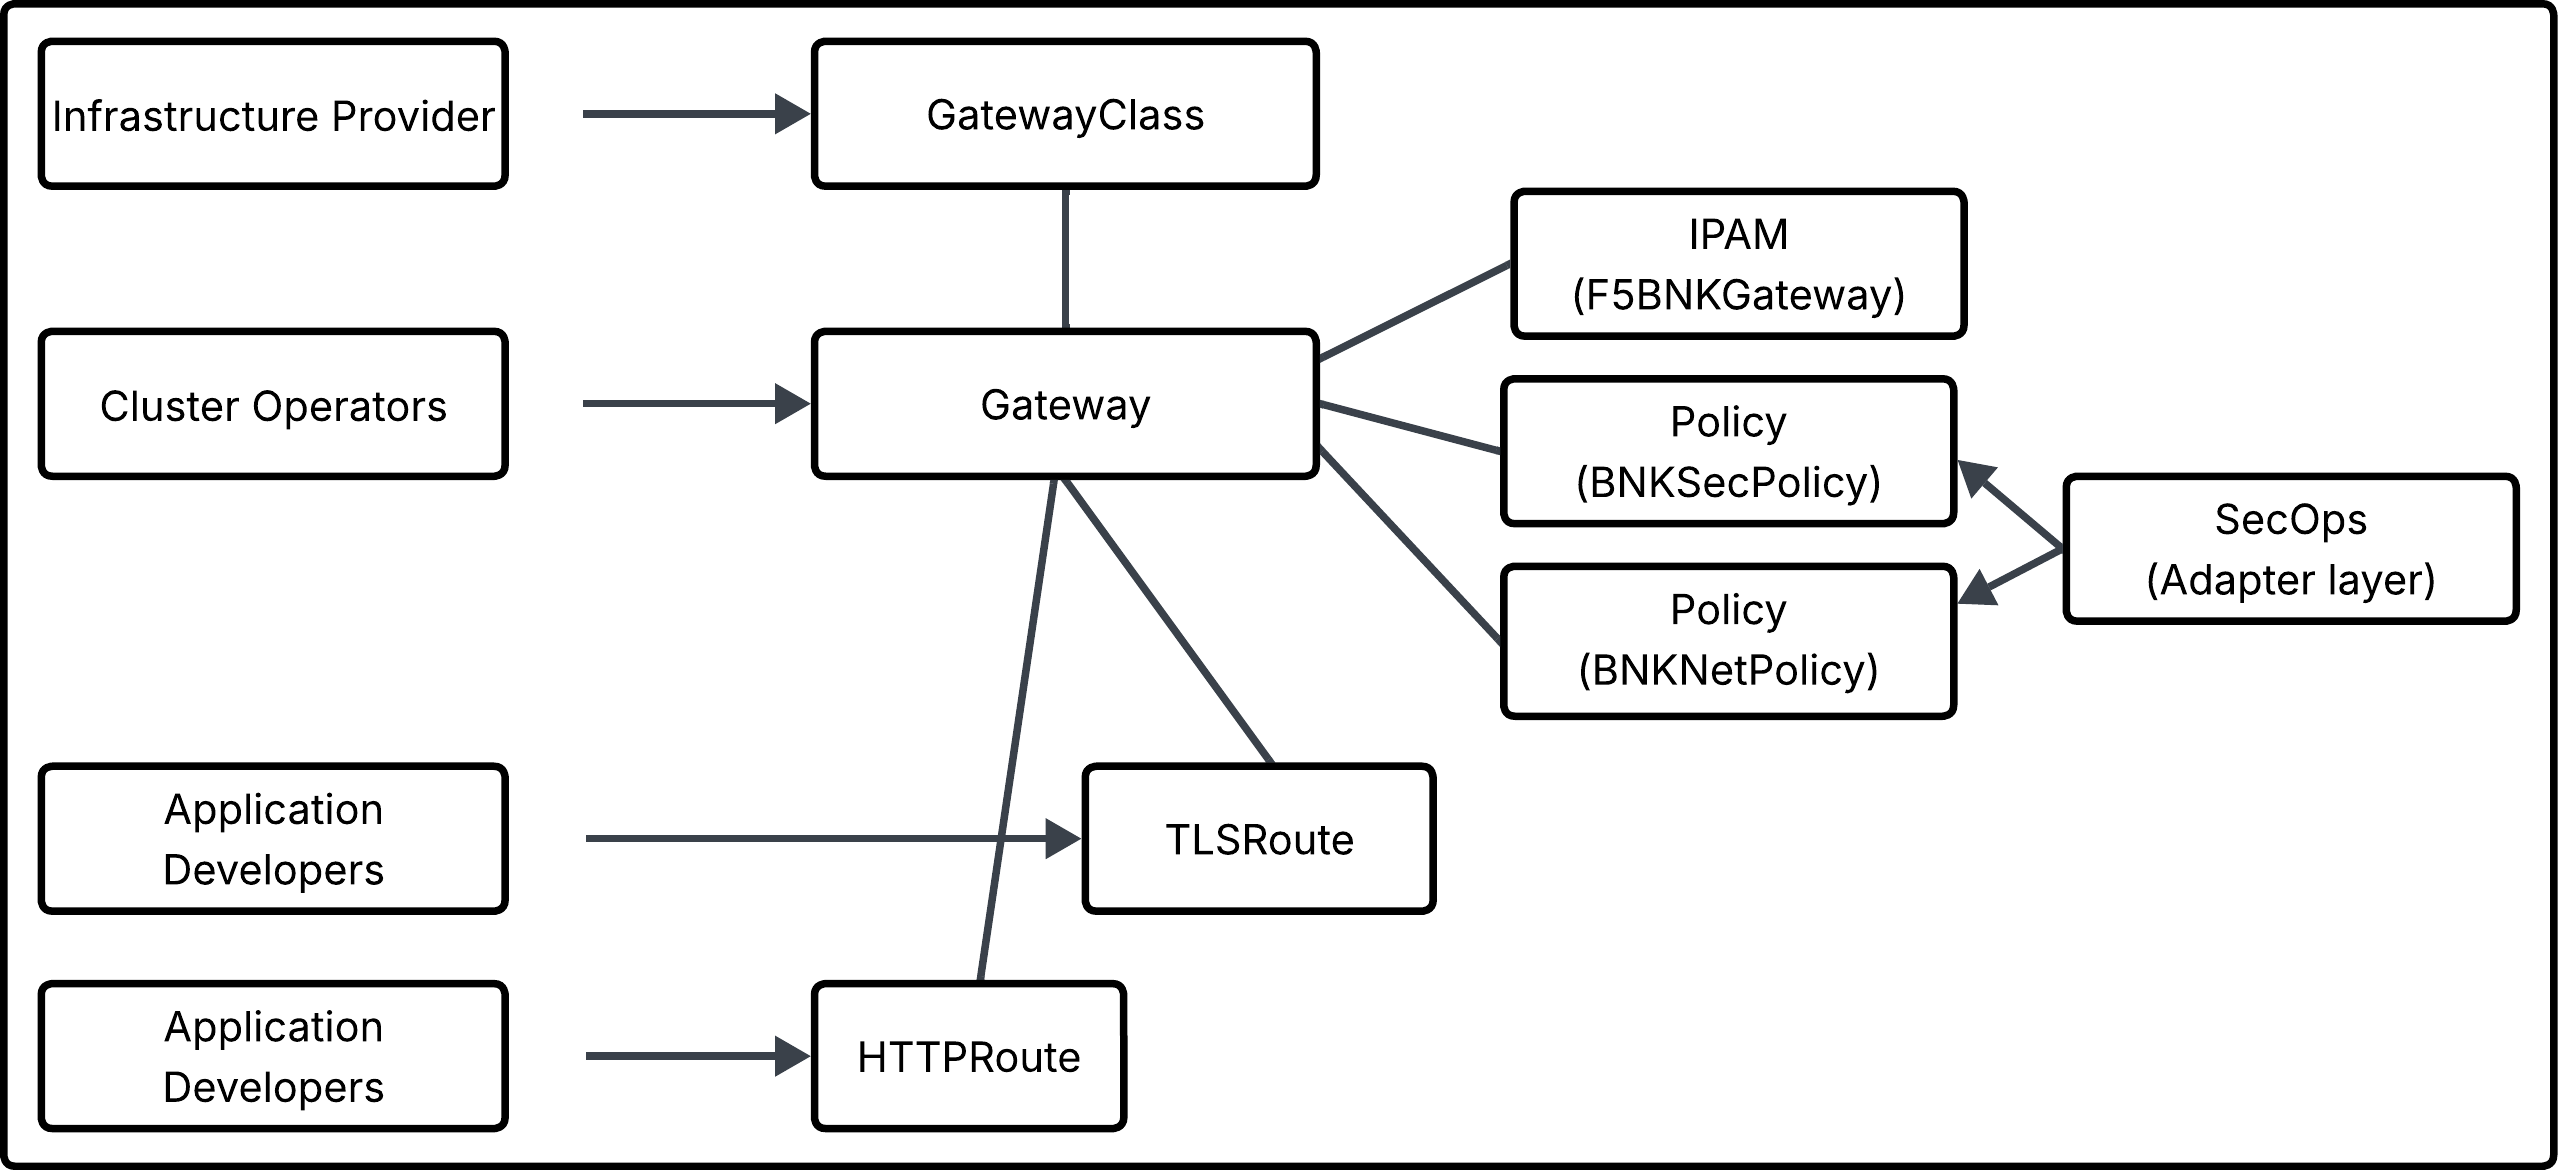
The Infrastructure Provider defines the GatewayClass. This cluster‑scoped resource describes a class of Gateways that the controller can deploy.
The Cluster Operator manages the Gateway resource. The Gateway defines how external traffic enters the cluster and how requests should be processed and forwarded.
The Application Developer creates route resources such as HTTPRoute, L4Route, and GRPCRoute. These routes define how traffic is matched and routed to backend services.
Gateway API Architecture
The diagram below shows how Gateway API works with BIG-IP Next for Kubernetes.
CNE Controller
The CNE-instance controller supports Gateway API CRDs and aligns with industry standards. The controller handles all F5 adapter CRDs, such as SecPolicy and NetPolicy, and manages attachments for resources such as F5BigFwPolicy and iRules using soft references.
Gateway API CRDs
BIG-IP Next for Kubernetes supports Gateway API features from v1.4.0. The CNE controller manages the following CRD types.
Adapter CRDs
F5 provides adapter CRDs to support customization and complexity management.
F5 CRDs
Gateway API Conformance Tests
Gateway API includes a full suite of conformance tests. These tests validate the controller’s behavior by creating Gateways and Routes using the selected GatewayClass.
See Conformance Report for details.
Using F5 IPAM Controller
You can use the F5 IPAM Controller (FIC) to automatically manage IP addresses for Gateway resources.
Firewall Policy in Gateway API
You can apply firewall policies to control traffic at the Gateway layer.
F5 iRules in Gateway API
You can use F5 iRules to customize traffic behavior.
High‑Speed Log (HSL) Profiles in Gateway API
You can configure HSL profiles in Gateway API to log events such as firewall actions.
Ingress DDoS Protection in Gateway API
You can apply DDoS policies to protect against protocol‑level attacks.
Supplemental Information
For more information on the Gateway API: