F5 Application Delivery Controller Solutions > Building the F5 Fabric > Module 1: BIG-IP Device Service Cluster Configuration Source | Edit on
Lab 2: Sync Only exercise
Objective: Add a sync only device group. You have already configured two VE’s in an Active/Active Configuration with two traffic groups. Add a 3rd VE. Create new Sync-Only group, and new Partition that will leverage new Sync-Only group. Create new SSL profile which will sync to all devices.
Prerequisites and Notes
Have at least 2 VE’s in an Active/Active Failover Configuration.
Note that for this exercise we will use three network interfaces (as in in the previous failover exercise)
1.1 = External Network Interface (Wan Side)
1.2 = Internal network interface (LAN Side)
1.3 = High Availability Network Interface
TASK 1 – Add HA Self IP to bigip3.lab
Go to Network -> Self Ips -> Create
Name:
192.168.1.12IP Address:
192.168.1.12Netmask:
255.255.255.0VLAN:
HAPort Lockdown:
Allow Default
Click Finished
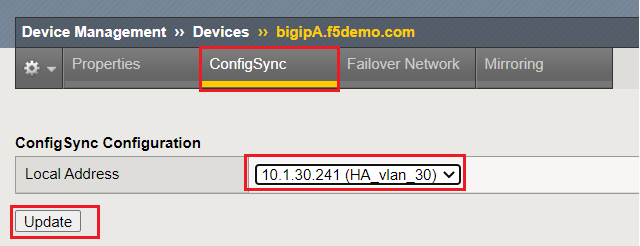
TASK 2 – Update Config-Sync Properties on bigip3.lab
Go to Device Management -> Devices
Click on then
bigip3.lab (Self)linkGo to ConfigSync tab
Select
192.168.1.12 (HA)in Local Address dropdownClick Update
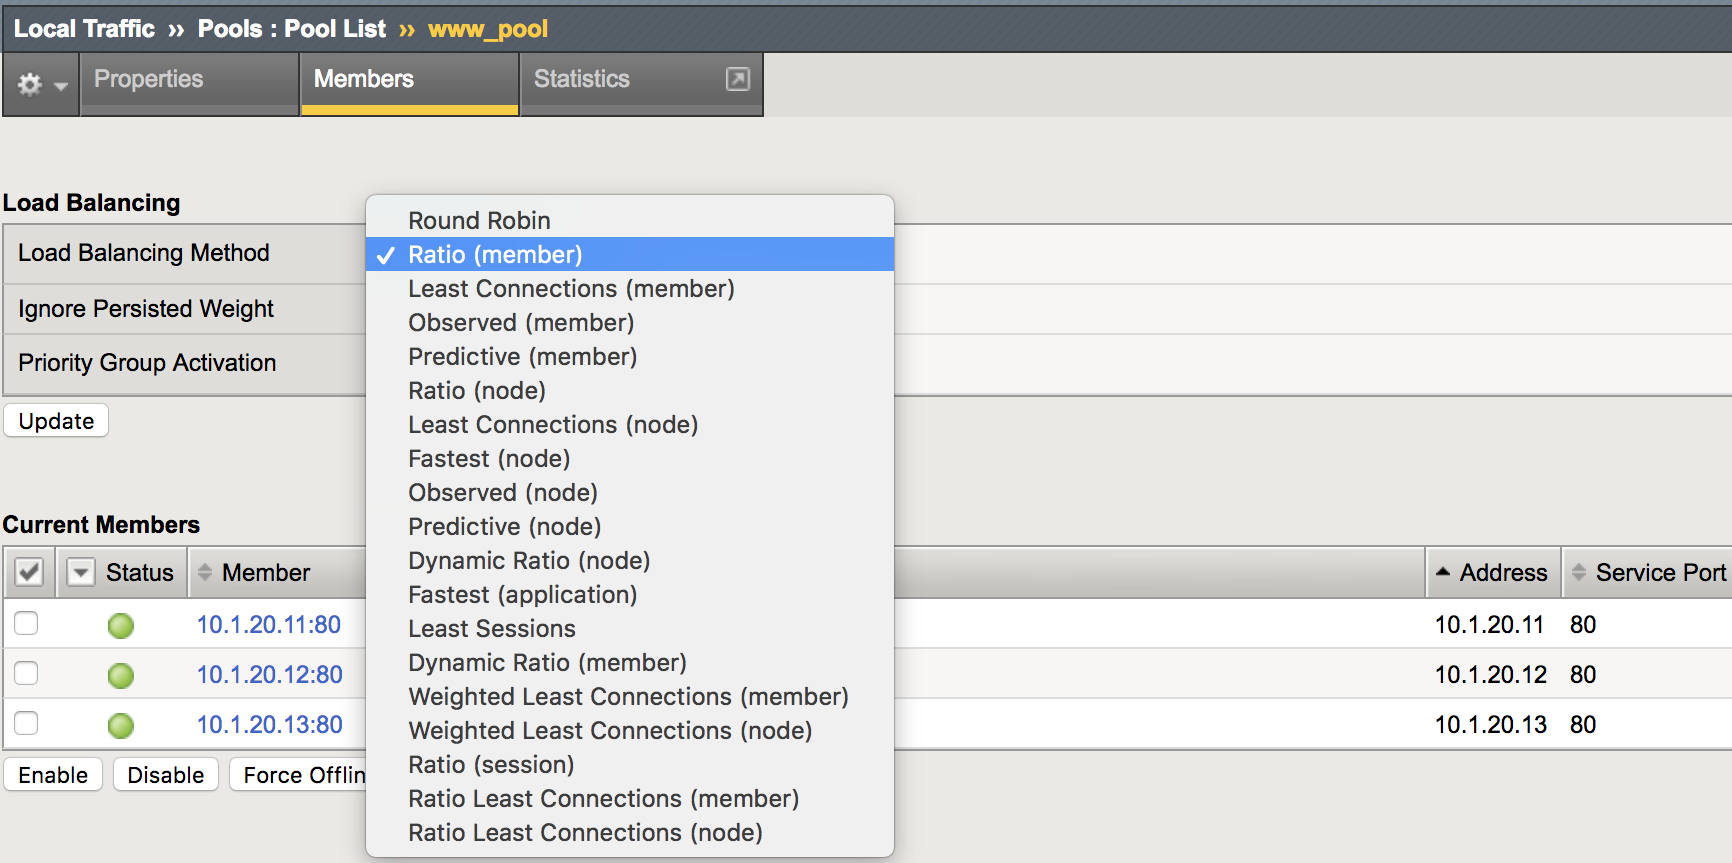
TASK 3 – Add bigip3 to peer list on bigip1
Go to Device Management -> Device Trust -> Device Trust Members -> Add

Click on Retrieve Device Information
Click Device Certificate Matches
Click Add Device
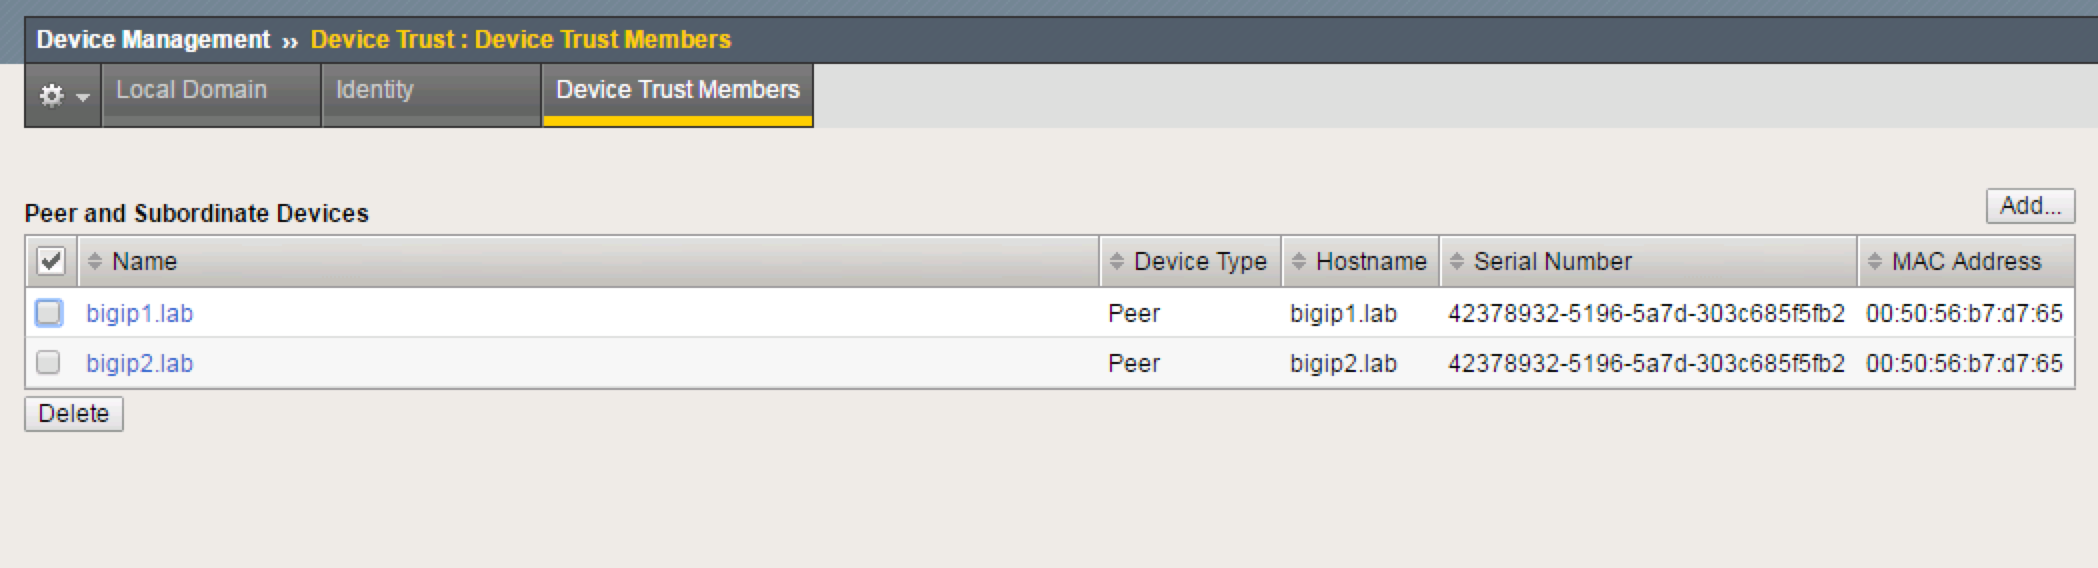
Go to bigip3 and verify bigip1 and bigip2 are now in the peer list
TASK 4 – Create New Sync Only Group
On bigip1:
Create a sync only group
Go to Device Management -> Device Groups -> Create
Name =
device_group_02_soGroup Type =
Sync-OnlyMembers = All 3 bigip’s
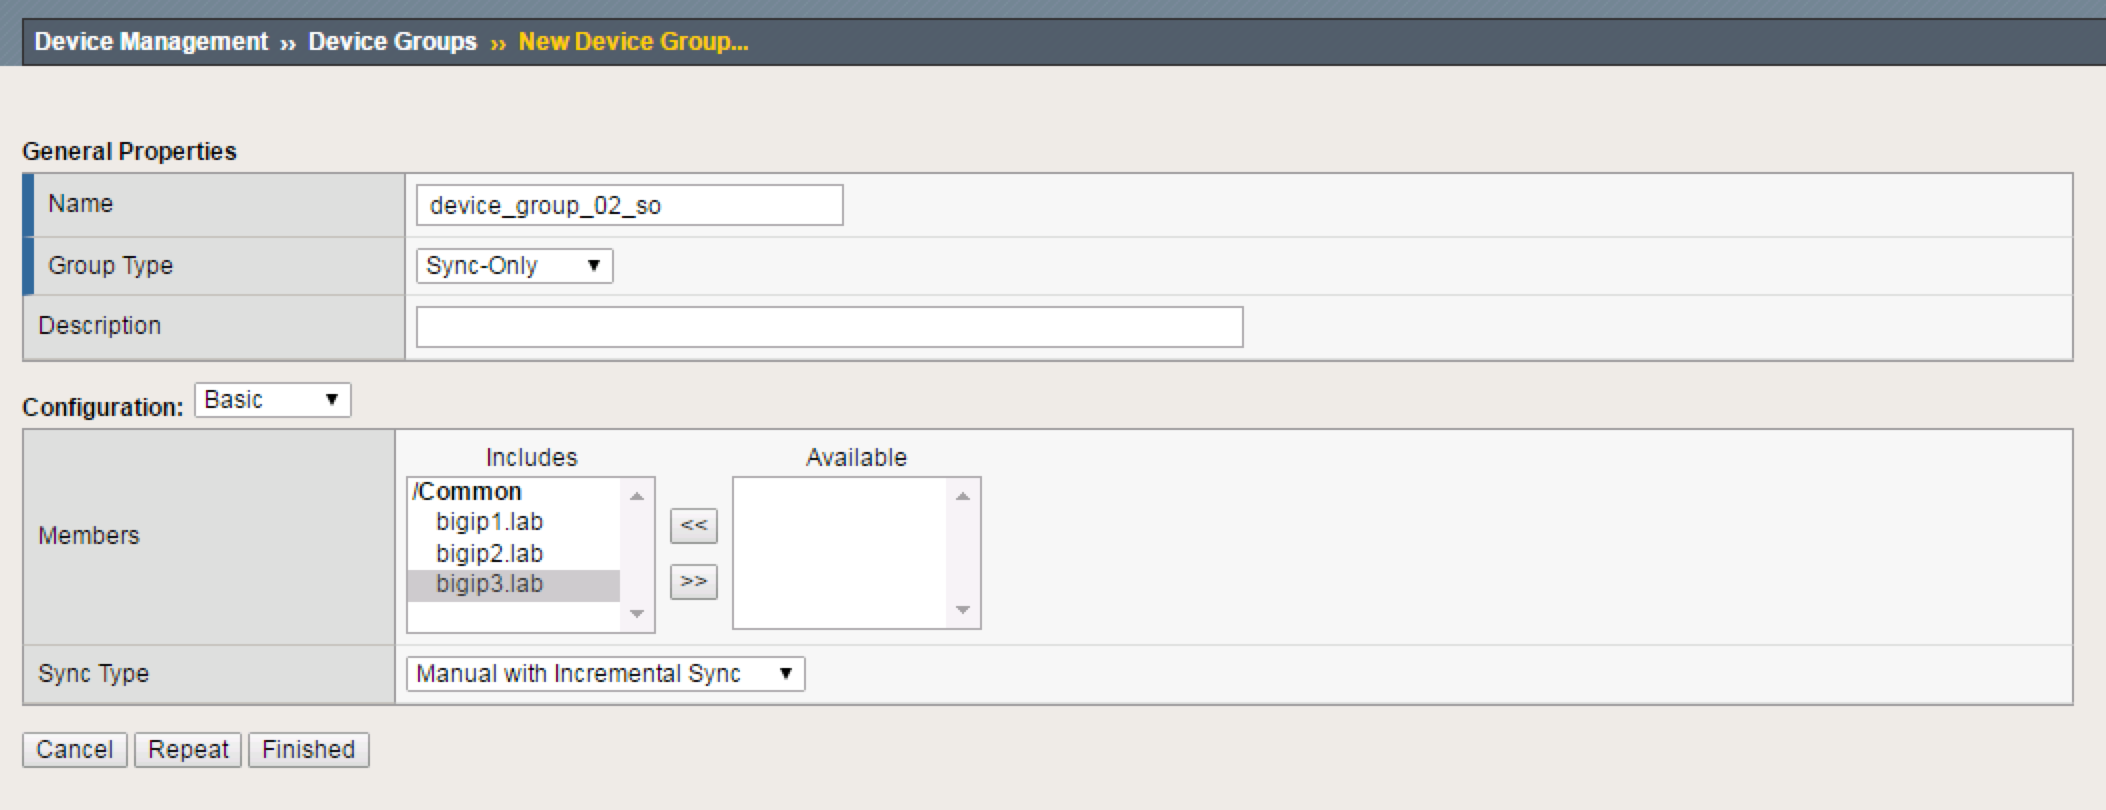
Click Finished
Perform initial sync
Click Awaiting Initial Sync in the upper-left of the GUI
Choose
device_group_02_so, then choosebigip1.Select Push the selected device configuration to the group and then click Sync
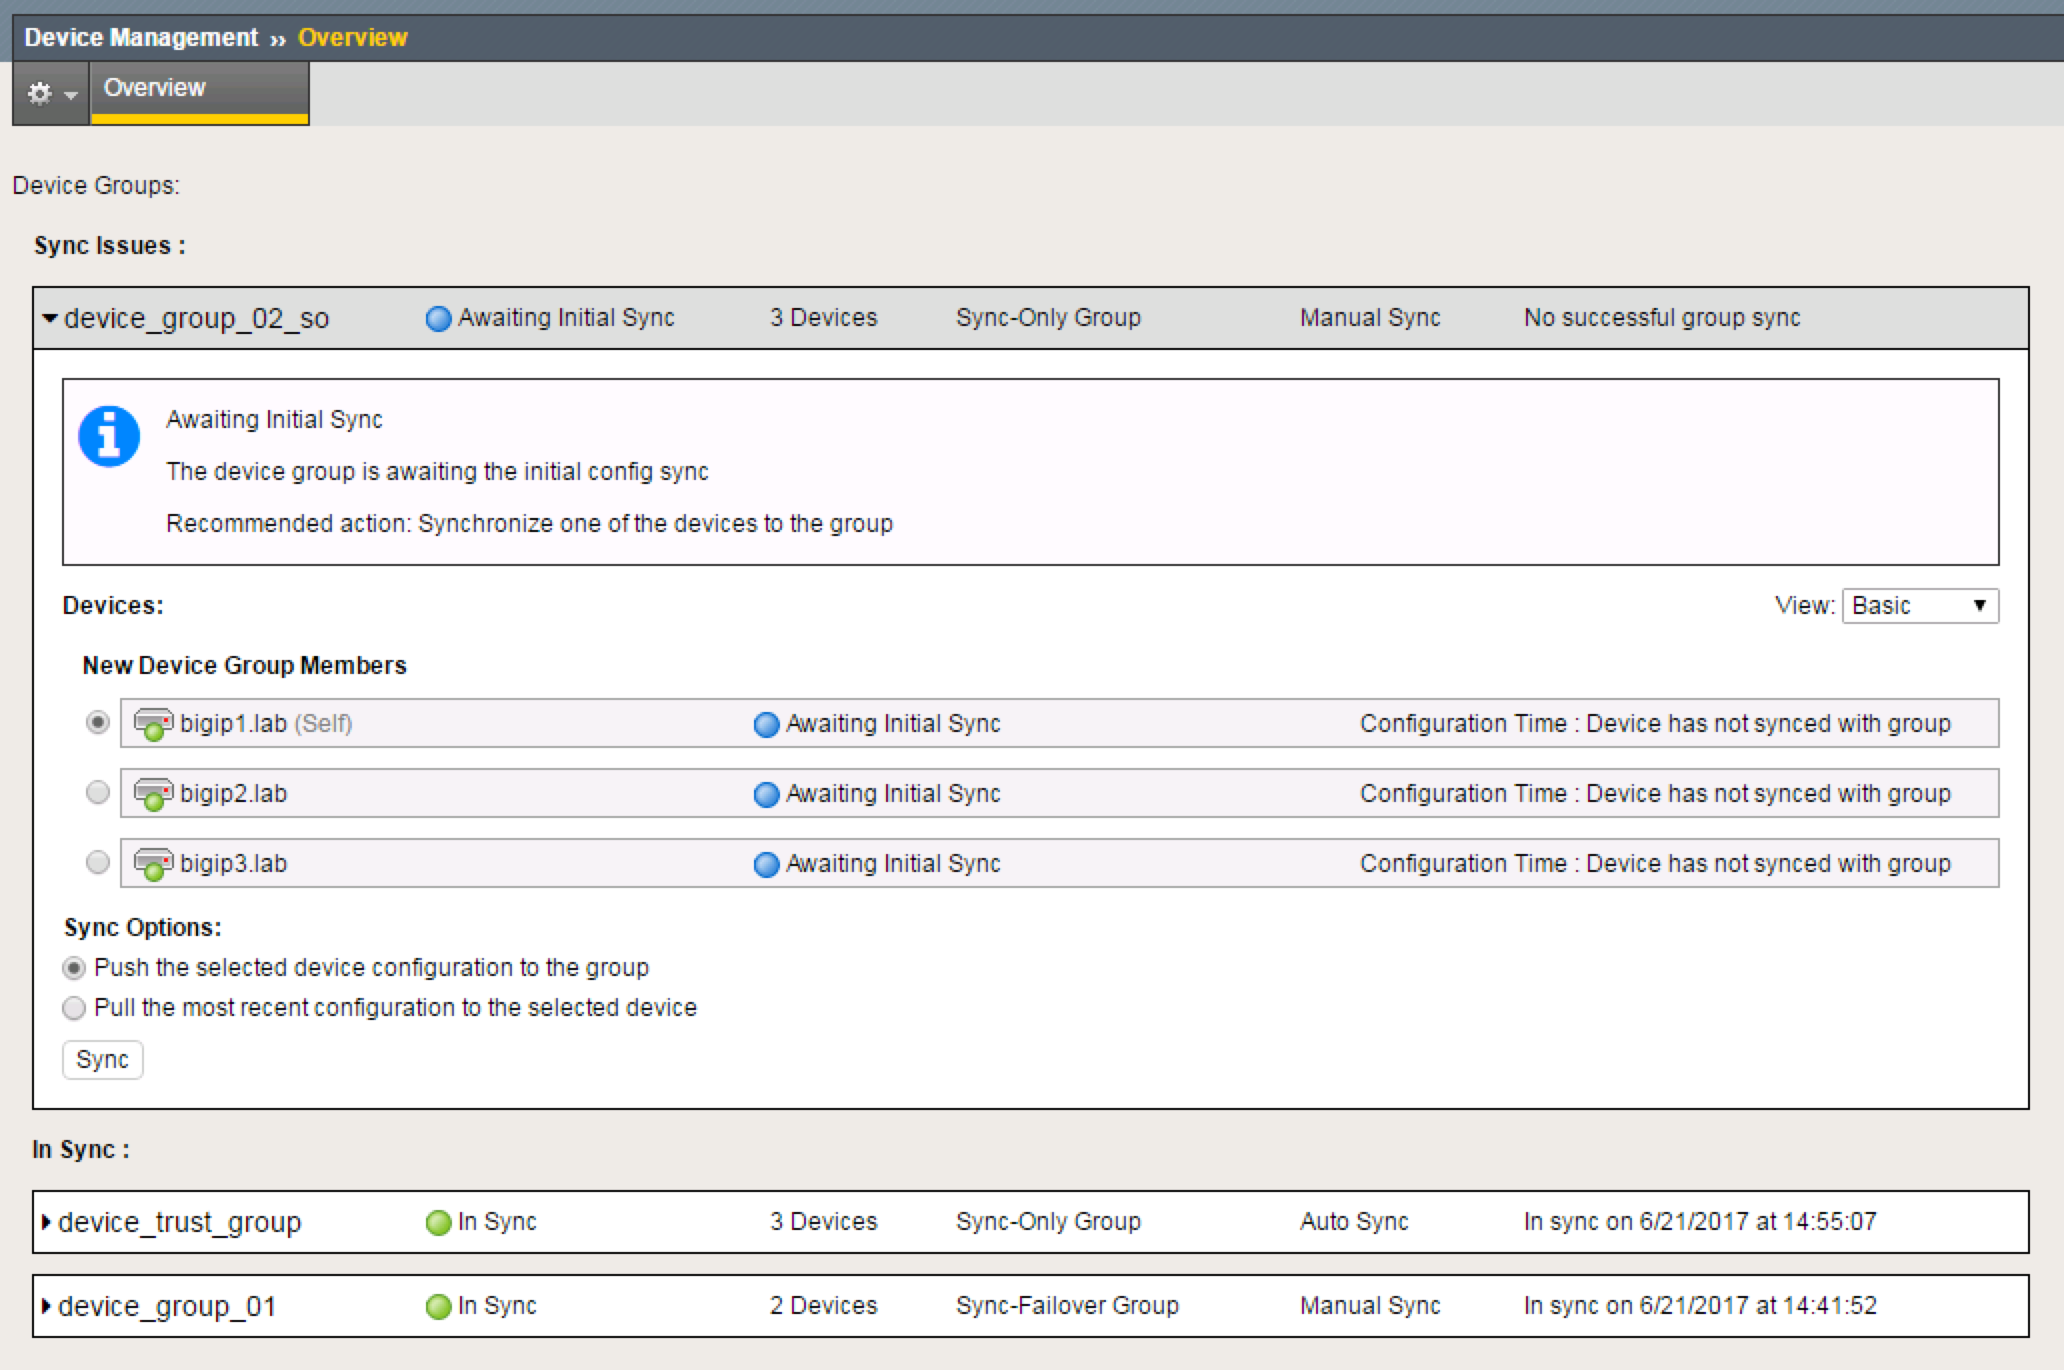
TASK 5 – Create New Partition and SSL Profile, Configure for Sync-Only
On bigip1:
Create new Partition
Go to System -> Users -> Partition List -> Create
Partition Name =
partition_02_soDevice Group = (uncheck "Inherit device group from root folder" box),
device_group_02_soTraffic Group =
None
Click Finished
Create new Client SSL Profile
Go to Local Traffic -> Profiles -> SSL -> Client
Change Partition to
partition_02_soin the upper-right of the GUI
Click Create
Name =
clientssl_02_labAccept all defaults
Click Finished
Sync Changes
On bigip2 and bigip3, confirm this Sync-Only clientssl profile has synced
Go to Local Traffic -> Profiles -> SSL –> Client
Choose
partition_02_soIs
clientssl_02_labthere?
What are some practical uses for Sync-Only device groups?