DNS > Class 1 - Intro to GSLB > 3. Datacenters Source | Edit on
3.2. Device Trust
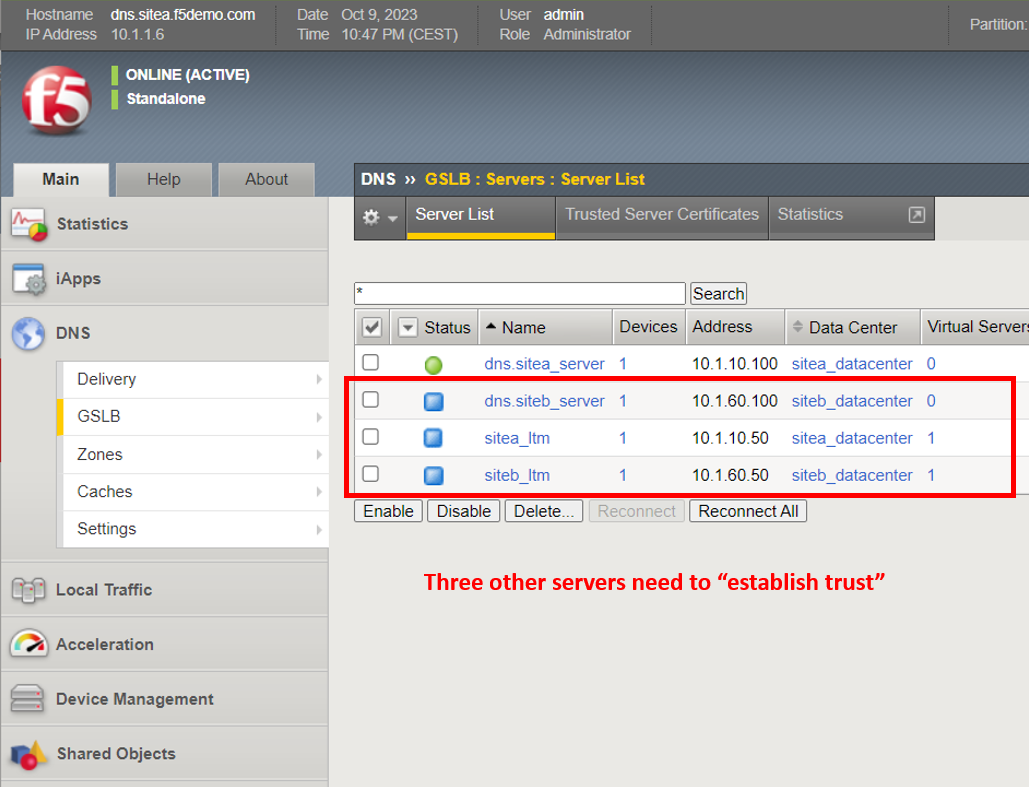
A mesh of F5 DNS servers need to exchange keys to establish a trusted mechanism for HA communications.
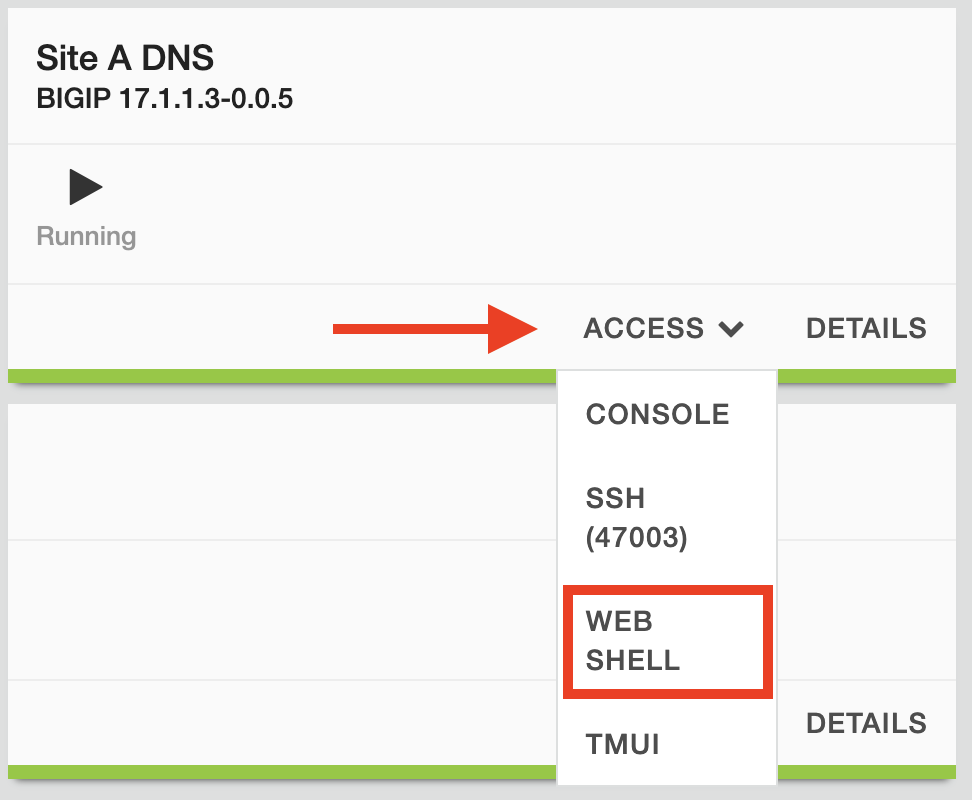
Launch Web Shell to Site A DNS
Run the following command:
Enter ‘yes’ for any connectivity prompts. When prompted for a password use “F5demo!!”.
TMSH
bigip_add
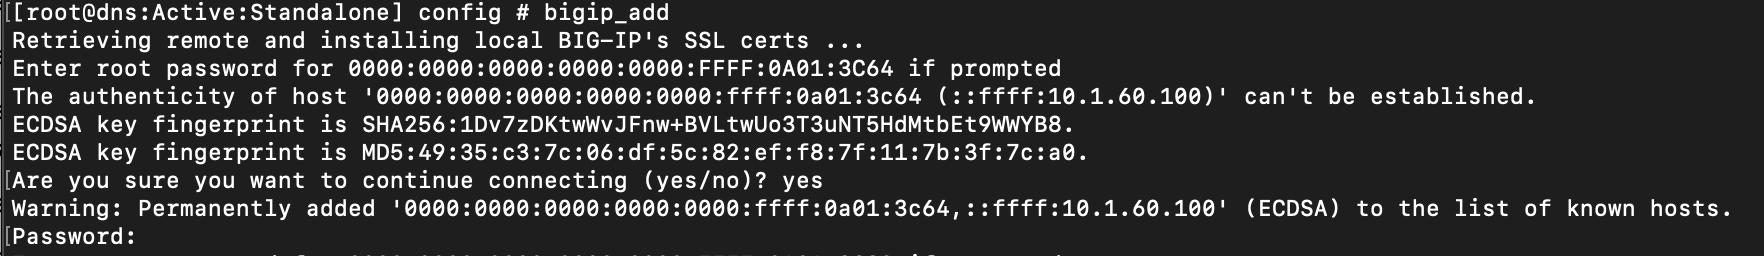
The ‘bigip_add’ command pulls the management certificate from the destination BIGIP devices for use during the encrypted iQuery channel setup between GSLB servers in the cluster. When running ‘bigip_add’ without any options, the command will be run against all BIGIP devices in the GSLB Server list using current username to connect to the endpoints. You can specifiy a connection username or endpoint IP(s) if needed.
bigip_add <user>@<endpoint_IP>
bigip_add <endpoint_IP>
bigip_add <endpoint_IP1> <endpoint_IP2>
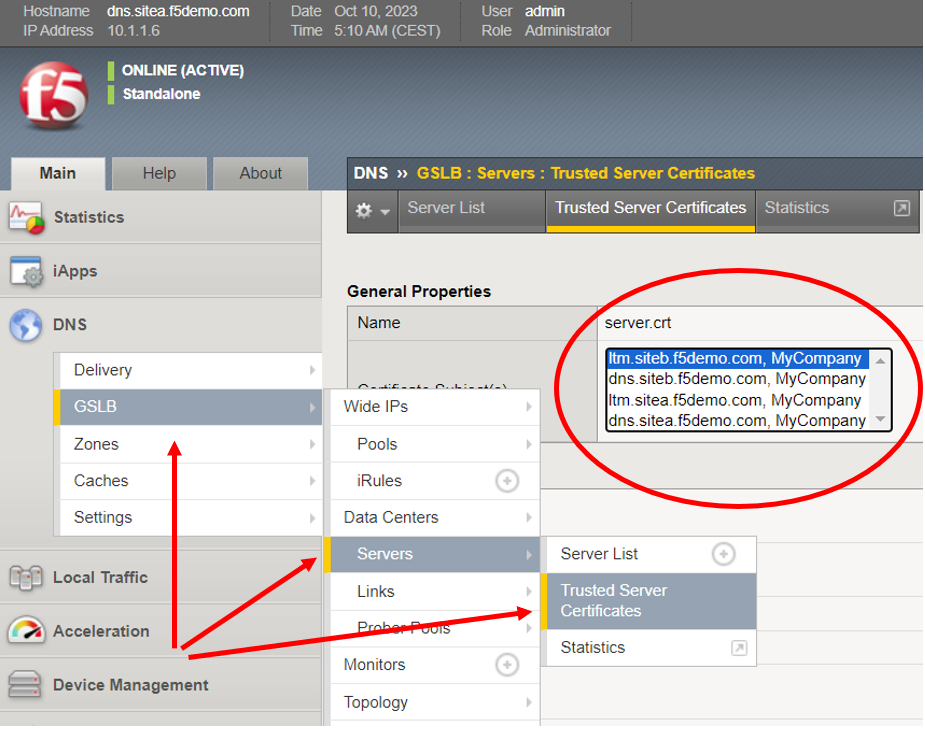
Navigate to: DNS ›› GSLB : Servers : Trusted Server Certificates